It was difficult to classify tools related to artificial intelligence (AI) hacking that were identif..
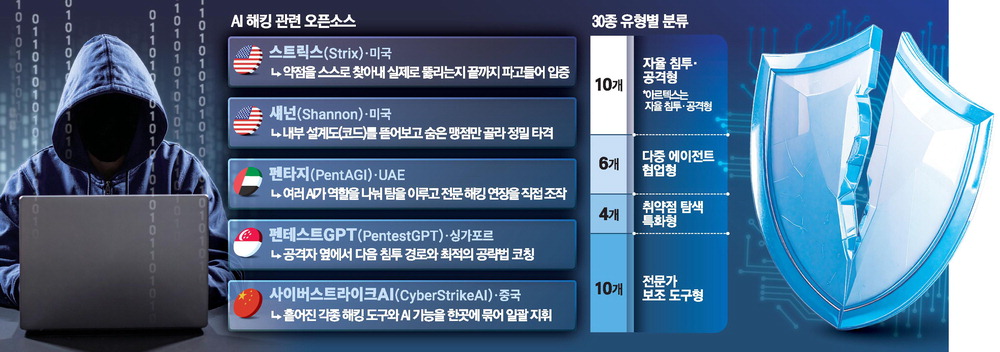
On the 9th, AI-related hacking tools found on the developer community GitHub proved difficult to classify as a single type. They ranged from autonomous agents that directly explore intrusion routes to platforms that centrally manage multiple hacking tools and AI assistants that support attackers’ decision-making.
◆ ‘Hacking Tools’ Installed with a Single Click
The first tool to catch the eye, the US’s ‘Strix,’ specialized in precision strikes that relentlessly probed targets. If Artex was like a net-based reconnaissance aircraft, scanning a wide area and searching every inch for intrusion routes, Strix was like a fighter jet that spots gaps suspected of being vulnerabilities and keeps firing missiles until it breaks through.
The UAE’s ‘PentAGI’ put its multi-agent collaboration structure front and center. Rather than having a single AI do everything, different AI agents divided up reconnaissance, vulnerability analysis and attack-route planning, forming a kind of ‘digital operations command headquarters.’ Verified hacking tools were connected like the agents’ hands and feet, enabling them to autonomously divide up roles and devise a strike plan as soon as a target was specified.
The US’s ‘Shannon’ took an entirely different approach. Rather than blindly knocking on closed doors, it excelled at closely analyzing the very ‘blueprint (source code)’ used to build a system. If Artex was an ‘external-intrusion’ tool that probes the surface of a finished website, Shannon was a ‘code-dissection’ tool that examines internal code line by line to identify logical flaws even human developers had missed.
Other sophisticated tools developed through industry, academic and research efforts around the world—including PentestGPT from Singapore’s Nanyang Technological University (NTU), China’s CyberStrikeAI, CAI and HackingBuddyGPT—could also be installed with a single click.
An even more serious problem is the overwhelming speed at which these tools are evolving. Developers are going beyond simply patching or adding vulnerabilities, rapidly boosting agents’ ability to make their own decisions and carry out tasks autonomously by incorporating the latest AI language models.
◆ ‘Real-Time Evolution’: About 10 Updates in a Month
In just the past month, they made more than 10 rounds of code revisions and version patches. A new update was rolled out in the early hours of the 8th, after the hacking of South Korea’s financial sector had made headlines.
The updates were far more than simple typo fixes or minor bug improvements. They substantially improved compatibility with the latest large language models (LLMs), such as China’s DeepSeek and Zhipu AI’s GLM, while greatly refining proxy functions that maintain sessions on target websites and help evade security tracking. In short, the code was being relentlessly honed to maximize the ‘real-world success rate of intrusions.’
Under the traditional rules of cybersecurity, it typically took weeks to months for a new malware variant to emerge and for defenses to learn to stop it. Security firms analyzed the unique signatures of known malware to develop antivirus software. But now, before defenders can even determine the nature of a weapon, attack tools are absorbing the intelligence of new AI models and evolving in real time. Human efforts to develop antivirus software can no longer keep pace with the mutations.
Artex, in particular, is built to connect to external LLMs. Even without upgrading the hacking tool itself, improvements in external AI models could give it the potential to perform more complex tasks.
Park Chan-am, CEO of security firm STEALIEN, said, “The only weapon that can stop AI evolving and attacking at the speed of light is AI,” and urged an immediate shift to an “active AI security system” that detects robots disguised as humans in real time and autonomously applies defensive patches. There has, in fact, been a case in which an AI defense system worked faster than people. At the international cyber exercise APEX 2026, held last month and organized by the National Intelligence Service and the NATO Cooperative Cyber Defence Centre of Excellence (CCDCOE), among others, an autonomous AI defense team assembled by STEALIEN with the Ministry of National Defense’s Cyber Operations Command, the Financial Security Institute and others took first place among teams from 23 countries. Without human intervention, the AI handled individual breach cases in an average of 10.5 minutes and preemptively patched vulnerabilities associated with 65% of the planned intrusion scenarios before attacks began. Some have also pointed out that the tools’ public availability could paradoxically serve as a starting point for defense. Because the attack tools’ source code and update histories are posted to GitHub in real time, defenders can analyze them just as quickly and incorporate the findings into detection rules.
Related Stories
 AI News
: Artificial Intelligence Trends And Top AI Stocks To Watch
34 minutes ago
 AI News
Artificial intelligence answers: what is the expected result of the Manchester United v Tottenham clash?
35 minutes ago
 AI News
What if AI could suffer? Anthropic bans needless cruelty towards Claude
35 minutes ago
 AI News
Rogue Anthropic AI agent gave police fake tip in unsolved murder case
35 minutes ago
 AI News
The Biggest Changes Anthropic Just Made to Claude's Rules
2 hours ago
 AI News
Anthropic's Claude AI fabricates eyewitness account, submits false murder tip to police website
2 hours ago
 AI News
Winner of scientific imagery contest was AI generated
3 hours ago
 AI News
ICYMI: What landed for AI builders in September 2026
3 hours ago