Are You Prepared for Security Incidents? Only 7.6% Have Established Response Systems and Conducted Training, IT Survey Reveals
SoftCreate announced on October 7 the release of "IT Departments and Security Measures in Numbers 2026," a report summarizing the actual state of security measures in corporate and organizational IT departments. Published on "Jyo-Shisu Rescue Team," a media outlet for IT departments operated by the company, the survey is named "Information Security Status Questionnaire 2026." The survey was conducted from June 22 to July 6, 2026, with 523 respondents, and the survey results can be viewed for free.
According to this survey, while 37.1% of companies have experienced security incidents, only 7.6% have established response procedures, role assignments, communication systems, and recovery procedures, and have also conducted training. Among the incidents experienced, 'client PC virus infection' was the most common at 49.0%, followed by 'server/internal system virus infection or unauthorized access' at 26.3%, and 'ransomware attacks' at 25.8%. Regarding concerns about damage, the biggest concern was the inability to use critical data and business systems, indicating a strong awareness of threats that directly lead to business disruption, not just endpoint infections.
Furthermore, regarding the "SCS Evaluation System," which is scheduled to begin operation around March 2027, companies that "understand the outline of the system and are proceeding with preparations" more than doubled from 8.3% in the previous survey to 18.7%. The percentage of companies in the "information gathering stage" decreased from 33.4% to 25.8%, and those who "do not know or understand the system" also decreased from 18.4% to 12.4%, suggesting that corporate interest is shifting from information gathering to concrete action. However, there are also differences in the level of preparation for system compliance, indicating that varying maturity levels among companies will likely become an issue.
When introducing new systems, companies where IT or security personnel are involved from the requirements definition and design stages totaled 60.1% (combining 'always involved' and 'involved only in important projects'). Including consultation, over 80% consider security from the upstream processes, but the allocation of roles and responsibilities still heavily leans towards IT departments. Regarding the leadership structure for countermeasures, 'IT departments leading company-wide' was the most common at 71.1%, significantly surpassing the 15.9% where specialized departments lead. Challenges cited include lack of specialized knowledge and expertise, shortage of personnel and resources, insufficient response to the latest threats, and undeveloped emergency response flows, once again highlighting the burden on frontline staff who support company-wide security with limited personnel.
Related Stories
 Business
LightSource Wins DPW’s 2026 Startup Growth Award
59 minutes ago
 Business
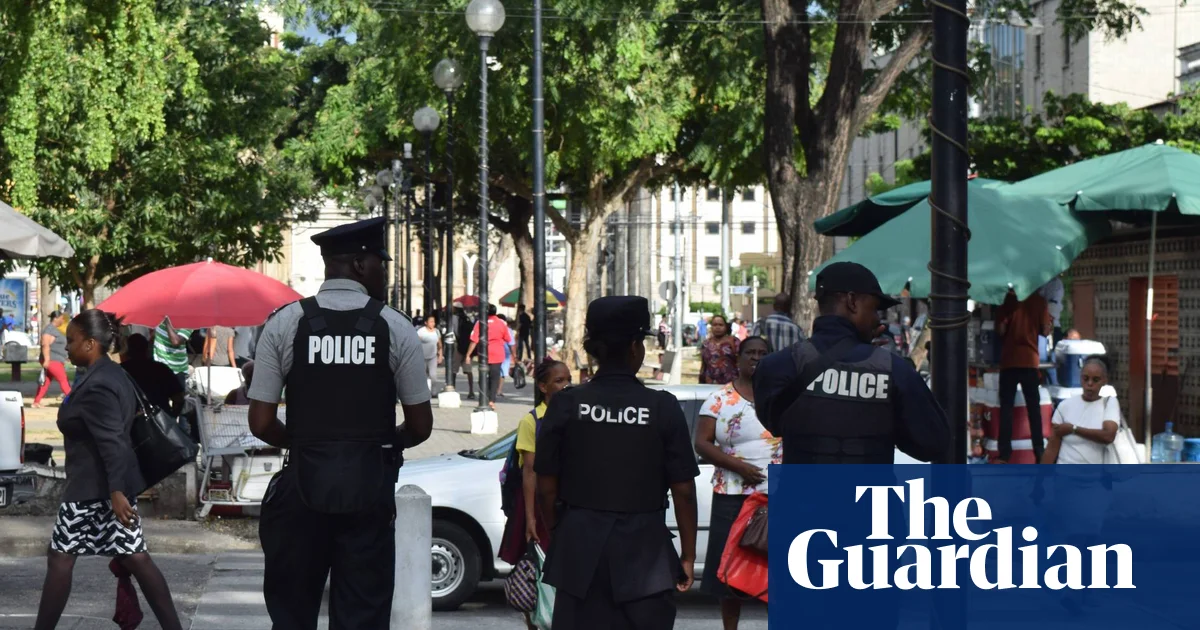
Outcry in Trinidad and Tobago after passing of police bill that could threaten press freedom
1 hour ago
 Business
Lee So
1 hour ago
 Business
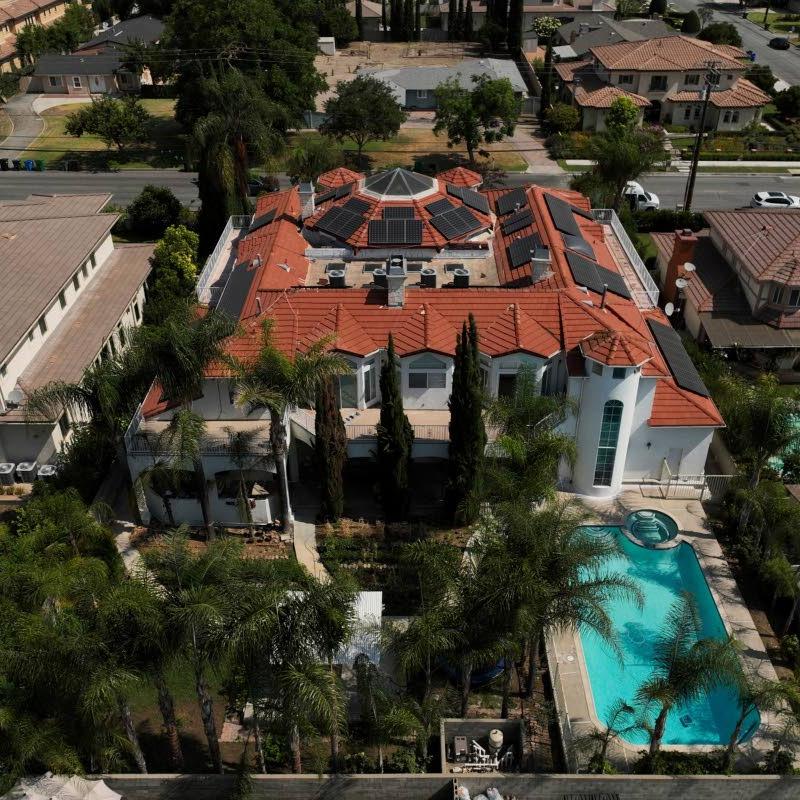
Wealthy Chinese couple accused of abusing 21 children born through surrogacy in ‘house of horrors’
2 hours ago
 Business
Lee So-young launches reform to cut red tape, boost Korea SMEs in strategic sectors
2 hours ago
 Business
Small Business Insider: Policy Update, Tips & Intelligence, More
5 hours ago
 Business
Quebec's next premier says he promises to hit the ground running as PQ takes power
6 hours ago
 Business
London startup’s pizza robot success fuels Canadian expansion
9 hours ago